SOC 2 Auditor in Australia: How to Choose the Right Firm
Only a licensed CPA firm can perform a SOC 2 examination and issue the report, which narrows your shortlist immediately. Australian companies can use an Australian CPA firm or a United States firm, and many use a US firm because SOC 2 originates with the American Institute of Certified Public Accountants. The firm that audits you cannot also be the consultant who prepares you, because that breaks the independence the report depends on. Everything else is a question of fit, price and availability.
That first point is worth stating plainly, because the Australian search results for this topic are full of firms offering SOC 2 certification. There is no such thing as a SOC 2 certificate. SOC 2 produces an attestation report containing an independent practitioner’s opinion. If a provider offers to certify you, they are either using loose language or selling readiness work under an audit label.
Who can do a SOC 2 audit?
A SOC 2 audit can only be performed by a licensed CPA firm. SOC 2 is a reporting framework owned by the American Institute of Certified Public Accountants, and the examination is conducted under AICPA attestation standards. The practitioner issues an opinion, and that opinion carries weight precisely because it comes from a firm bound by professional standards, independence rules and peer review.
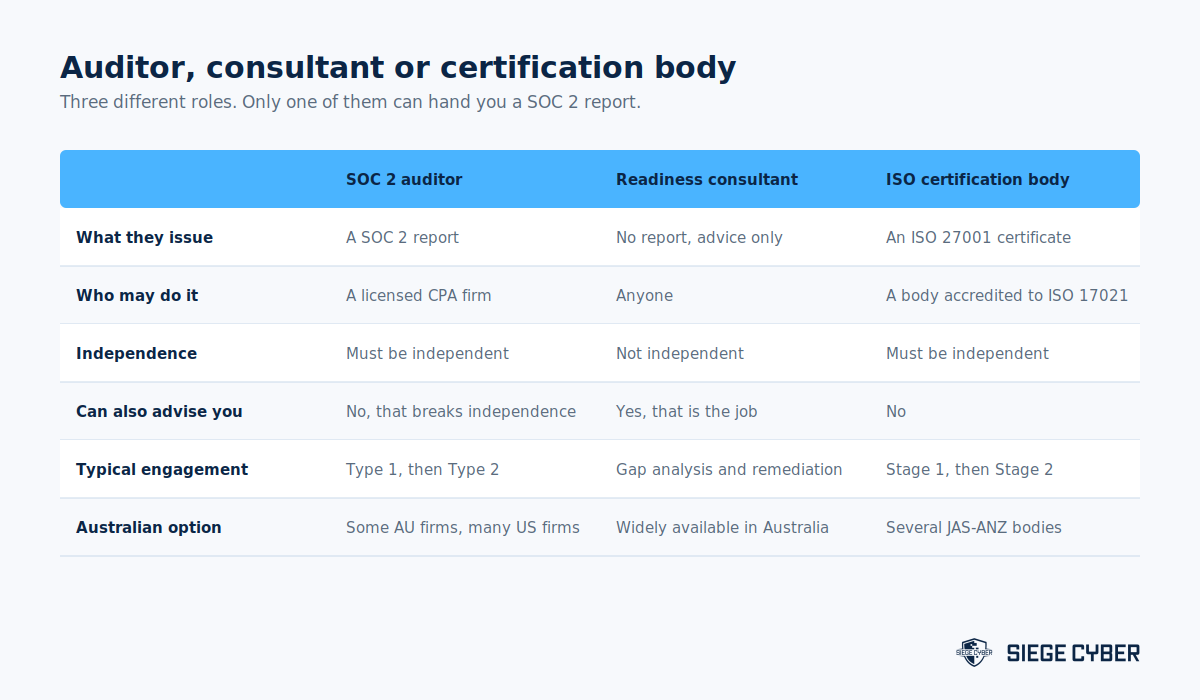
This is the structural difference between SOC 2 and ISO 27001. ISO 27001 certificates are issued by certification bodies accredited to ISO/IEC 17021. SOC 2 reports are issued by CPA firms. A consultancy, a managed service provider or a compliance platform can help you get ready for either, but neither can issue the outcome.
You can read more about what the framework covers on the AICPA’s SOC suite of services page, and our guide to which Trust Services Criteria apply covers what your report should be scoped to include.
Do you need an Australian SOC 2 auditor?
You do not need an Australian SOC 2 auditor. An Australian company can be audited by a CPA firm licensed in the United States, and a great many are, because the framework is American and the deepest pool of experienced SOC 2 practitioners sits there. Several Australian firms also perform SOC 2 examinations, including the large accounting networks and a number of mid tier practices.
The real trade off is timezone and familiarity against price and experience. An Australian firm is easier to meet with, understands your local context, and will not schedule your walkthroughs at midnight. A US firm may have audited fifty companies that look exactly like yours. Neither is automatically the right answer for a 30 person Australian SaaS business.
| Consideration | Australian CPA firm | United States CPA firm |
|---|---|---|
| Working hours | Your business hours | Usually your evenings or early mornings |
| SOC 2 experience | Growing, varies widely by firm | Often very deep |
| Understanding of local context | Privacy Act, local customers, local suppliers | Usually needs explaining |
| Cost | Varies, often mid to high | Wide range, including low cost providers |
| Recognition with your buyers | Fully recognised | Fully recognised |
| Practical risk | Fewer firms, so availability can be tight | Communication gaps across timezones |
How do you tell a SOC 2 auditor from a SOC 2 consultant?
You tell a SOC 2 auditor from a SOC 2 consultant by asking one question: will you be signing the report? An auditor is a CPA firm that performs the examination and issues an opinion. A consultant prepares you for that examination by finding gaps, writing policies and helping you build the evidence trail. Both are useful. Using the same firm for both is not permitted, because independence is what makes the opinion meaningful.
In Australia the language gets blurry because some providers offer both readiness and an audit through an affiliated firm. That arrangement is worth questioning closely. Ask who holds the CPA licence, who signs the opinion, and whether the readiness team and the audit team are separate organisations.
If you want a consultant first, that is usually the right order. Our guide to a SOC 2 readiness assessment explains what a readiness engagement should produce before you approach an auditor at all.
What should you ask a SOC 2 auditor before you sign?
Ask a prospective SOC 2 auditor about licensing, experience with businesses your size, what their fee covers, how long the report takes after fieldwork, and what happens if they find something during the examination. The answers to the last two questions are where the differences between firms show up most clearly.
- Are you a licensed CPA firm, and where? Ask for the licence details. This is a reasonable question and any legitimate firm answers it immediately.
- How many SOC 2 examinations have you completed for companies our size? A firm whose experience is all enterprise will bring enterprise process to a 30 person company.
- What is in the fee, and what is not? Check whether a Type 1, a bridge letter, or a second year of the examination is included or quoted separately.
- How long between the end of fieldwork and the final report? Weeks matter when a customer contract is waiting on the report.
- What happens if you find an exception? Exceptions are normal. You want a firm that tells you early rather than at draft report stage.
- Who is on the team? Ask whether the people doing the fieldwork are the people you met in the sales conversation.
- Will you review our readiness work? An auditor cannot advise you, but they can tell you whether your scope and criteria selection look sensible before you commit.
Buyers will read the resulting report closely. Our guide to how to review a SOC 2 report shows what a sophisticated customer looks for, which is a useful lens when choosing who writes yours.
How long does a SOC 2 audit take?
A SOC 2 Type 1 examination usually takes two to four weeks of auditor time once you are ready, and a Type 2 requires an observation window of three to twelve months before fieldwork begins. The total elapsed time from starting readiness to holding a Type 2 report in your hand is commonly six to twelve months for an Australian business doing it for the first time.
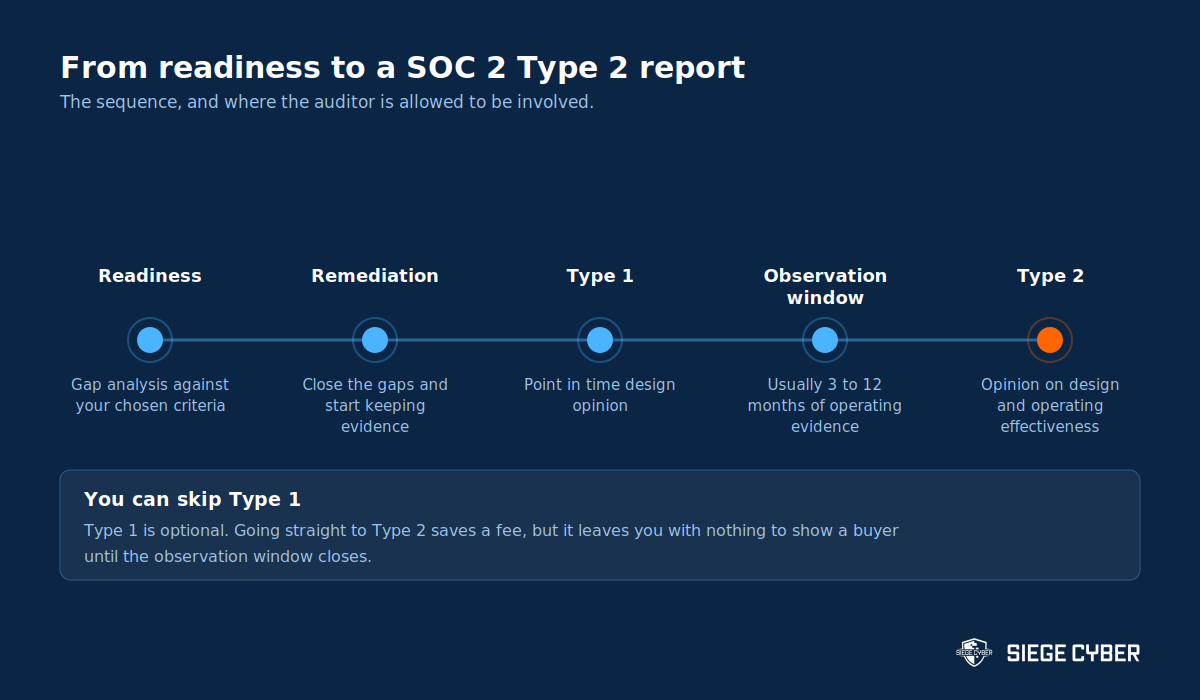
The observation window is the part people underestimate. A Type 2 report covers how controls operated over a period, so a three month window means three months of access reviews actually happening, tickets actually being raised, and backups actually being tested. Starting the window before your controls are actually running is the most common cause of exceptions in a first report. Our comparison of SOC 2 Type 1 and Type 2 covers how to choose the window length.
What is the equivalent of SOC 2 in Australia?
There is no Australian equivalent of SOC 2, and no Australian regulator requires it. The closest comparison is ISO 27001, which is an internationally recognised certification available from Australian certification bodies and is more commonly requested by Australian and European buyers. SOC 2 is requested most often by North American customers and by Australian buyers whose own compliance programme was built around it.
For many Australian businesses the honest answer is that ISO 27001 serves the same commercial purpose at similar effort, and you only need SOC 2 if a customer has asked for it by name. Our side by side comparison of ISO 27001 and SOC 2 sets out the difference, and our guide to SOC 2 for Australian SaaS companies covers when it is worth doing.
Common questions
Who can do a SOC 2 audit?
Only a licensed CPA firm can perform a SOC 2 examination and issue the report. SOC 2 is owned by the American Institute of Certified Public Accountants and the examination is conducted under AICPA attestation standards. Consultants, managed service providers and compliance platforms can prepare you for the examination, but they cannot issue the opinion, and the firm that prepares you cannot also audit you.
Are there SOC 2 auditors in Australia?
Yes. Several Australian CPA firms perform SOC 2 examinations, including the large accounting networks and a number of mid tier practices. The pool is smaller than in the United States, so availability can be tight around reporting periods. Australian companies are also free to engage a United States CPA firm, and the resulting report is recognised identically by buyers either way.
How much does a SOC 2 audit cost?
SOC 2 audit fees vary widely by firm, scope and the number of Trust Services Criteria in your report, and readiness work is usually a separate cost again. Ask every firm to quote the full cycle rather than the first examination alone, because year two arrives twelve months later. Our Australian cost guide breaks down what drives the total, including the parts that are not the auditor’s fee.
How often are SOC 2 audits done?
SOC 2 Type 2 reports are typically produced annually, because customers want a report covering a recent period and most will not accept one that has aged past twelve months. The gap between the end of one report period and the start of the next is usually covered with a bridge letter from you, not from your auditor. Annual reporting is an ongoing commitment, not a one off project.
What is the equivalent of SOC 2 in Australia?
There is no direct Australian equivalent and no Australian law requires SOC 2. ISO 27001 is the closest comparison and is more commonly requested by Australian and European buyers. Australian government work has its own pathways, including IRAP assessment for systems handling government data. SOC 2 is worth pursuing when a customer has specifically asked for it, rather than as a default choice.
Can a consultant sign my SOC 2 report?
No. Only the licensed CPA firm that performed the examination can issue the report and sign the opinion. A consultant who claims they can certify you against SOC 2 is describing something that does not exist. If a provider offers readiness and audit as one package, ask who holds the CPA licence and whether the two teams are separate firms.
Where to start
Before you contact a single auditor, settle two things: which Trust Services Criteria your report needs to cover, and whether you are going straight to Type 2. Those two decisions change the quote you receive from every firm, and getting them wrong is expensive to unwind once fieldwork has started.
Siege Cyber does readiness work, not audits, which means we can tell you honestly whether you are ready before an independent firm tells you for a fee. You can see what that involves on our SOC 2 service page, or get in touch to talk through scope. Our guides to the SOC 2 audit process and what SOC 2 costs in Australia cover the rest of the journey.