What We Test
Siege Cyber provides penetration testing across the full spectrum of your technology environment. We specialise in web application security and are widely recognised as Australia's best web application penetration testers, but we also cover network infrastructure, APIs, cloud environments, mobile applications, and wireless networks.
Web Application Penetration Testing (Our Speciality)
This is where we excel. Web penetration testing is our core strength and what we are known for across Australia. Whether you need web app penetration testing for a customer portal or SaaS penetration testing for a multi-tenant platform, we do not just run automated scanners and call it a day. We manually test your applications the way a skilled attacker would: probing authentication and session management, testing authorisation controls, hunting for injection flaws (SQL, command, XPath, LDAP), exploiting business logic vulnerabilities, analysing API security, and identifying insecure configurations.
We follow the OWASP Web Security Testing Guide and OWASP Top 10, but we go deeper. We understand modern frameworks (React, Vue, Angular), serverless architectures, microservices, and how attackers exploit the gaps between components. Our SaaS penetration testing engagements are designed to uncover the flaws that matter most in shared, cloud-hosted environments, while our web app penetration testing covers everything from internal tools to complex partner-facing platforms. Whatever your application, we will find the vulnerabilities before the attackers do.
If you need web application penetration testing in Australia, this is what we do best.
API Penetration Testing
APIs are the backbone of modern applications, and they are consistently targeted by attackers. We test REST, GraphQL, SOAP, and WebSocket APIs for authentication and authorisation flaws, injection vulnerabilities, excessive data exposure, rate limiting issues, and insecure endpoints. API security is not the same as web application security. We know the difference.
Network Penetration Testing (External and Internal)
External network testing simulates an attacker on the internet trying to breach your perimeter. We identify exposed services, misconfigurations, unpatched systems, and paths into your environment. Internal network testing assumes an attacker has gained access (via phishing, compromised credentials, or insider threat) and evaluates how far they can move laterally, what they can access, and whether they can escalate privileges.
Cloud Infrastructure Penetration Testing
Cloud environments (AWS, Azure, GCP) introduce unique security challenges. We test IAM policies, role assumptions, privilege escalation paths, storage misconfigurations (S3 buckets, Blob storage), insecure managed services, and API security. Cloud penetration testing is not just network testing in the cloud. It requires specific expertise in cloud-native attack vectors. We have it.
Mobile Application Penetration Testing
We test iOS and Android applications for insecure data storage, weak cryptography, insecure communication, reverse engineering risks, and server-side API vulnerabilities. Mobile apps are often the weakest link in an otherwise secure system.
Wireless Network Penetration Testing
We assess the security of your wireless infrastructure, including WPA2/WPA3 configurations, guest network segmentation, rogue access point detection, and wireless intrusion prevention. If your office has Wi-Fi, it is part of your attack surface.
Our Process
We have conducted hundreds of penetration tests for Australian businesses. Here is how we do it.
1. Scoping and Rules of Engagement
We meet with your team to define the scope (what we are testing), the testing window (when we can test), the rules of engagement (what is off-limits), and the testing methodology (black box, grey box, or white box). You leave this phase with a clear understanding of what will happen, when it will happen, and what to expect.
2. Reconnaissance and Information Gathering
We gather information about the target environment using open-source intelligence (OSINT), DNS enumeration, subdomain discovery, and other reconnaissance techniques. For grey box and white box tests, we also review architecture documentation, source code, and access credentials to accelerate testing.
3. Vulnerability Identification and Manual Testing
This is where the technical work happens. We use a combination of automated scanning tools (to identify low-hanging fruit) and manual testing techniques (to find the complex, high-impact vulnerabilities that automated tools miss). We probe authentication mechanisms, test authorisation controls, attempt injection attacks, analyse business logic, exploit misconfigurations, and identify paths to privilege escalation or data exposure.
4. Exploitation and Impact Assessment
For critical and high-risk vulnerabilities, we attempt controlled exploitation to demonstrate impact and validate the severity. We never cause intentional damage or access production data unnecessarily, but we do prove that the vulnerability is exploitable and document exactly what an attacker could achieve.
5. Reporting and Debrief
We deliver a detailed penetration testing report that includes an executive summary (for non-technical stakeholders), a technical findings section (with evidence, reproduction steps, and impact analysis), a risk rating for each vulnerability, and remediation guidance. We also conduct a debrief session with your team to walk through the findings and answer questions.
6. Retesting (Optional, 2-4 Weeks After Remediation)
Once you have remediated the identified vulnerabilities, we offer optional retesting to confirm the fixes are effective and no new issues were introduced. Many of our clients include retesting as part of the initial engagement.
Who This Is For
This service is built for Australian SaaS companies, technology businesses, financial services firms, healthcare organisations, and any business that handles sensitive data or operates critical systems.
You are a good fit if:
- You need to meet compliance requirements that mandate regular penetration testing (ISO 27001, SOC 2, PCI DSS, APRA CPS 234, Essential Eight)
- Your board, investors, or customers are asking for independent security validation
- You are launching a new application or major feature and want to test it before it goes live
- You have been breached before and want to ensure it does not happen again
- You are undergoing a security audit and need evidence of regular testing
- You are serious about security and want an honest assessment from people who actually know how to break things
If you are looking for web application penetration testing in Australia, Siege Cyber is the team you want. This is our speciality, and we are known across the industry for the depth and quality of our web app testing. We find the vulnerabilities that other testers miss because we understand modern web architecture, application security, and how attackers think.
Why Choose Siege Cyber
Australia's leading web application penetration testers. This is what we are known for. When Australian companies need their web applications properly tested, they come to us. We have spent over 20 years breaking web applications, and we know where to look. If you need the best web app penetration testing in Australia, this is it.
20+ years of offensive security experience. Our Technical Director, Peter Stewart, has spent over two decades in hands-on cybersecurity roles, including network security engineering and penetration testing. We are not junior testers following a checklist. We are experienced professionals who understand both the attack surface and the business impact.
We understand Australian compliance requirements. Whether you need testing for Essential Eight, ISO 27001, SOC 2, APRA CPS 234, or PCI DSS, we know what auditors and regulators expect. We deliver reports that satisfy compliance requirements while also providing genuinely useful security insights.
Manual testing, not just automated scans. Automated vulnerability scanners are useful, but they miss the complex, high-impact vulnerabilities that require human judgement. We use automation to accelerate reconnaissance and baseline scanning, but the real value comes from manual testing by experienced penetration testers who know how to think like attackers.
Clear, actionable reporting. Our reports are written for two audiences: technical teams who need to fix the issues, and business leaders who need to understand the risk. You get detailed technical findings with reproduction steps and proof-of-concept exploits, plus an executive summary that explains what matters and why.
Frequently Asked Questions
How often should we do penetration testing?
It depends on your risk profile and compliance requirements. Most standards (ISO 27001, SOC 2, PCI DSS, Essential Eight) require annual penetration testing at minimum. High-risk environments or rapidly changing applications may benefit from quarterly or bi-annual testing. We also recommend testing before major product launches, after significant infrastructure changes, or following a security incident.
What is the difference between a vulnerability scan and a penetration test?
A vulnerability scan is an automated tool that checks for known vulnerabilities based on signatures and version detection. It is useful but shallow. A penetration test includes manual testing by experienced security professionals who probe for business logic flaws, chained exploits, and complex vulnerabilities that automated scanners cannot find. Penetration testing provides much deeper assurance and is what compliance frameworks require.
Do you test production environments or only staging?
We can test either, depending on your preference and risk tolerance. Many clients prefer us to test production environments because that is where real vulnerabilities exist, but we take extreme care to avoid disruption. For high-availability systems, we can test staging environments that closely mirror production, though this may miss environment-specific issues.
What happens if you find a critical vulnerability during testing?
If we identify a critical vulnerability (such as unauthenticated remote code execution or direct database access), we notify you immediately via phone or secure communication channel, rather than waiting for the final report. This allows you to respond quickly and mitigate the risk before an attacker discovers the same issue.
Will penetration testing disrupt our operations?
We design our testing to minimise disruption. For production environments, we avoid denial-of-service attacks, destructive payloads, and anything that could cause outages. That said, some testing (particularly exploitation) may trigger security alerts or temporarily affect performance. We coordinate closely with your team to schedule testing during low-traffic windows if needed.
Do we get a retest after we fix the vulnerabilities?
Retesting is typically offered as an optional add-on. Some clients include it in the initial engagement. Retesting confirms that your remediation efforts were successful and that no new vulnerabilities were introduced during the fixes. We typically conduct retesting 2-4 weeks after you have completed remediation.
How much does penetration testing cost?
The cost depends on the scope, type of testing, size of the target environment, and duration of the engagement. Web application tests typically range from a few thousand dollars for a small application to tens of thousands for complex, multi-tier systems. Network and cloud testing costs vary based on the number of hosts and complexity. Contact us for a detailed quote based on your specific needs.
Ready to Find Your Vulnerabilities?
Penetration testing is not about proving you are secure. It is about finding the weaknesses before an attacker does and giving you a clear plan to fix them. The longer you wait, the greater the risk that someone else finds them first.
Book a free 30-minute consultation with our team. We will assess your environment, recommend the appropriate type of testing, and provide a detailed quote with no obligation. If you need web application penetration testing in Australia, you are in the right place. This is our speciality and what we do better than anyone else.
Our Penetration Testing Methodology
Every engagement follows a documented penetration testing methodology aligned to CREST and to the OWASP and PTES testing standards, so the work is repeatable and the report holds up in front of an auditor or a customer security questionnaire.
We agree scope and rules of engagement first, then work through reconnaissance, vulnerability identification, manual exploitation and post-exploitation. Automated scanning has its place at the discovery stage, but a pen test is defined by what a person does next: chaining low-severity findings into something that actually matters, and testing whether your security controls detect and stop the activity rather than simply whether a port is open.
Findings are rated on real business impact rather than raw CVSS, because a critical on an isolated test box and a medium on an internet-facing authentication flow are not the same problem. Each one carries reproduction steps and a specific remediation action, and we retest once you have made the fixes.
Where Social Engineering Fits
Technical testing tells you whether your systems hold. It does not tell you whether your people would spot a phishing campaign. Most incidents we are called into began with a stolen credential rather than an exploit, which is why phishing attacks remain the most dependable way into an Australian business.
If that is the part of the threat landscape you are most concerned about, our employee phishing testing runs realistic phishing tests against your staff and reports who needs support rather than who to blame. Plenty of clients run both: a pen test to strengthen your security at the technical layer, and phishing testing to close the human gap.
Choosing a Penetration Testing Provider
If you are comparing providers rather than ready to scope, we have written an honest guide to choosing a penetration testing company in Australia, covering what CREST accreditation actually tells you and the six questions that get different answers from different firms. There are local guides too, for Brisbane, Sydney and Melbourne.
Specialised Testing
Beyond the core areas above, two kinds of testing come up often enough to be worth naming, usually because a customer contract or a regulator has asked for them specifically.
IoT and Connected Device Testing
If your business builds, deploys or depends on connected hardware, the device is only part of the attack surface. We test the firmware, the communication between the device and its cloud backend, the provisioning and update process, and the authentication model that decides which device is allowed to talk to which account. The failures we find most often are not exotic: hardcoded credentials, update channels that are not verified, and backend APIs that trust whatever the device sends.
Physical Security and Social Engineering
A technical test assumes the attacker is on the network. Physical testing asks a different question: could someone walk into your office, plug into a port, sit in an unlocked meeting room and work from there? Combined with social engineering, it tests the assumptions your technical controls quietly rely on. Most Australian businesses do not need this every year, but if you hold sensitive data on site or are working towards DISP, it belongs in the programme.
What Penetration Testing Costs
We publish our prices, which is still unusual in this market. A single engagement generally falls between $3,400 and $16,500 excluding GST, quoted as a fixed price before any work starts. A basic website test sits at the lower end. A large web application, or an internal network test with Active Directory in scope, sits at the upper end.
What moves a quote is scope and depth: how many IP addresses or user journeys are in scope, how many roles we have to test as and across, and how complex the application is underneath. A retest after you have remediated is included rather than billed separately, which is worth checking when you compare quotes, because it often is not.
The full breakdown by test type, including what sits at each end of every range, is on our penetration testing pricing page. If testing is being driven by a certification rather than by a specific worry, our compliance package pricing may be the better starting point, since external testing is included in those.
Penetration Testing Across Australia
We are an Australian company, based in Brisbane, working with clients nationally. The great majority of penetration testing is delivered remotely, because that is how the attack would happen, so where your business sits rarely changes the engagement or the price.
Where location does matter is internal network testing, physical assessments and anything requiring us on site, and for the conversations that go better face to face. We work regularly with businesses in Sydney, Melbourne, Brisbane, Perth, Adelaide and Canberra, and we cover regional centres as well. The full list is on our locations page.
One practical note for Defence and government suppliers: being an Australian owned and operated company, with Australian based testers, is frequently a contractual requirement rather than a preference. If that applies to you, it is worth confirming early with any provider you are considering, including us.
How We Compare to Other Australian Penetration Testing Companies
Most penetration testing firms in Australia will tell you the same things, so here is what we think actually separates one from another, stated as criteria you can apply to anyone, not only to us.
Where the accreditation sits. CREST accreditation can be held by an individual tester or assessed and held at company level. Ours is held at company level, which means the processes, the methodology and the reporting were examined, not just one person's exam result. Ask any provider which of the two they hold. The answers differ more than you would expect.
How much of the testing is done by a human. Every provider runs automated tooling, and so do we. The question is what happens afterwards. Business logic flaws, broken access control between user roles and chained vulnerabilities are not found by scanners, and they are where the serious findings usually are. If a quote looks unusually low, this is normally what has been removed.
Whether the retest is included. A report full of findings is not the outcome you wanted. A clean report after remediation is. We include the retest. Many firms charge for it, which can make an apparently cheaper quote the more expensive one.
Who writes the report, and for whom. You need two documents in one: something your engineers can act on, with evidence and reproduction steps, and something your board or your customer's security team can read without translation. Ask to see a sample report before you sign.
Whether they will tell you not to buy. If a vulnerability scan is the right thing for your situation this year, we will say so. A provider who recommends the largest engagement regardless of what you describe is selling, not advising.
We have written this up at greater length, with the six questions worth asking, in our guide to choosing a penetration testing company in Australia.
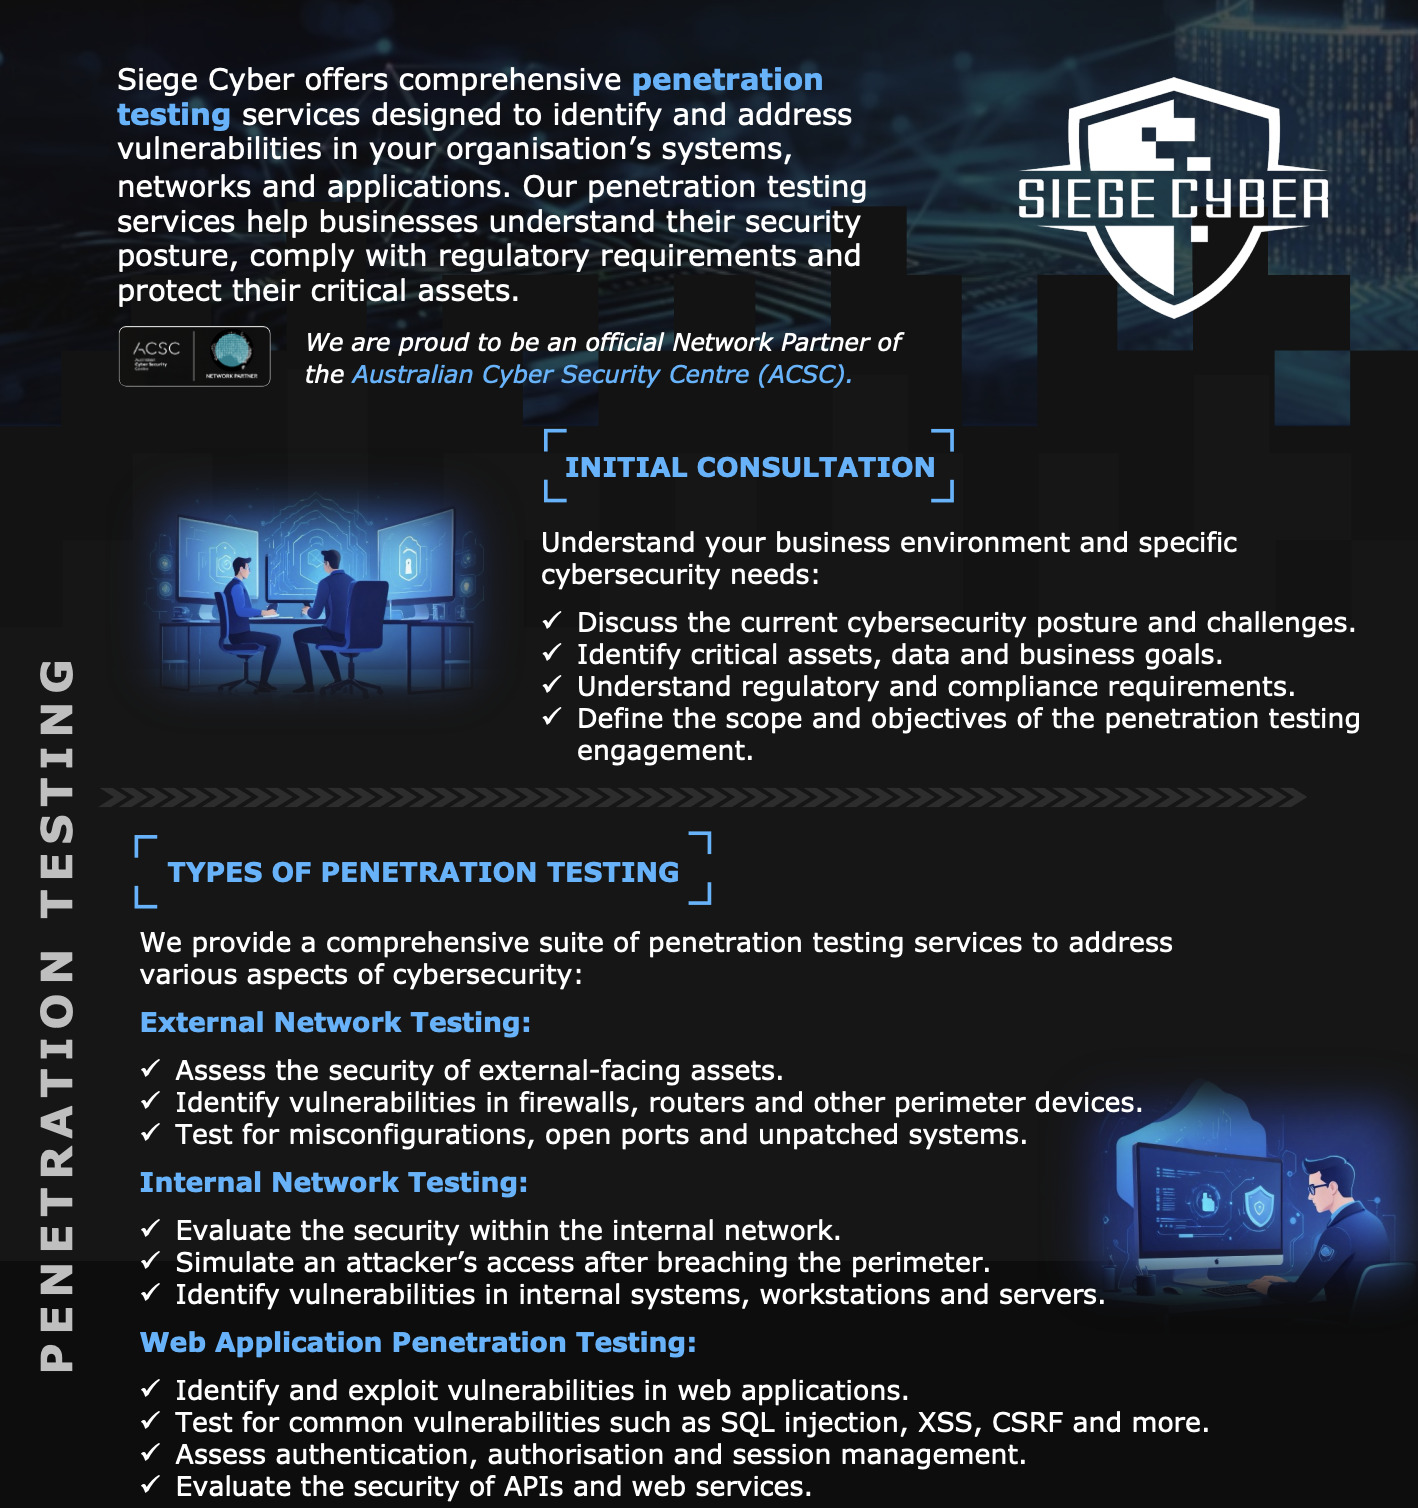
Uncover vulnerabilities and strengthen your defences with Siege Cyber's expert penetration testing services. Our penetration testers meticulously test your systems to identify and mitigate security risks, ensuring your digital assets remain protected against potential threats. For an in-depth look at how our penetration testing services can enhance your cybersecurity posture, download our datasheet today.